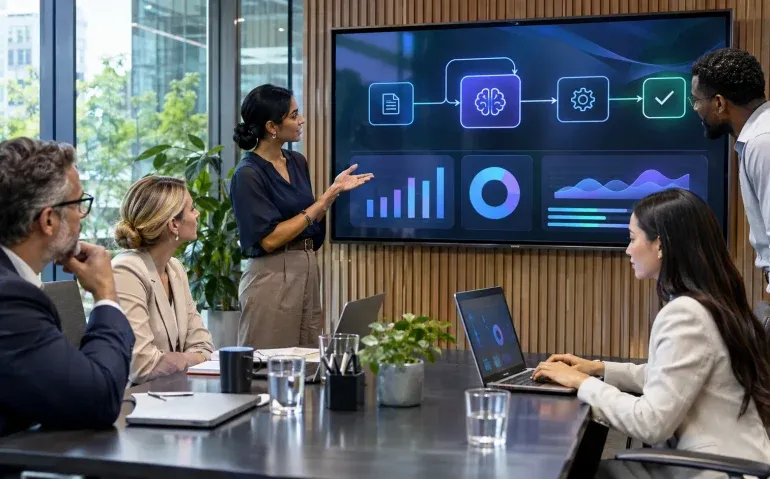
Enterprise AI is moving from answering questions to carrying out work. Early business tools mainly summarized documents, drafted emails, or answered employee questions. Newer systems can use approved software tools, retrieve company information, and complete steps in a workflow. The shift toward autonomous digital workers could change how routine office tasks are handled, but it also raises a more demanding question: how can a company delegate useful work without giving software more authority than it can safely manage?
From conversation to action
A chatbot usually responds to a prompt with text. An agent can take a goal, break it into steps, call tools, and evaluate what happened. In an enterprise setting, that might mean searching a knowledge base, preparing a draft report, checking a ticket, or routing a request to the right team. The agent’s value comes from connecting language and reasoning to existing business systems.
Digital workers will not necessarily replace a job or team. More often, they may take on a bounded portion of a workflow that currently involves copying information between applications or handling predictable requests. People can then focus on exceptions, customer conversations, decisions, and work requiring context. The quality of that arrangement depends on whether the task is well understood and the system can stop when it reaches an uncertain point.
Why companies are moving in this direction
Many organizations have experimented with generative AI through standalone chat tools, but business value is harder to realize when employees must copy answers into other systems and verify every detail manually. An agent connected to approved tools can reduce that friction. It might collect information from several sources, prepare a proposed action, and ask a person to approve it.
The strongest candidates are tasks that are repetitive, measurable, and reversible. A company may let an agent classify a support request or prepare a purchase order draft, while requiring human approval before a refund, payment, account closure, or customer-facing commitment. This staged approach gives teams a chance to measure accuracy and operational value before expanding an agent’s role.
What an agent needs to work reliably
An enterprise agent needs access to accurate information, well-designed tools, and clear rules. Company documents should have owners and update processes so that the agent does not cite outdated policies. Business systems should provide narrow actions rather than broad, unrestricted access. The agent should record what it did and which sources informed its answer, making it possible to investigate mistakes.
Good workflow design also defines what the agent cannot decide. It should know when to ask for missing information, when to escalate to a person, and which actions always require approval. A system that handles routine cases well but recognizes its limits may be more valuable than one that attempts every task with confidence.
Governance becomes operational
As agents gain the ability to read and change records, AI governance must move beyond a general policy document. Teams need an inventory of agents, models, data sources, tools, permissions, owners, and business purposes. They should assess privacy, security, reliability, and the consequences of an incorrect action before deployment.
Canadian financial regulator OSFI advises institutions to treat AI components—including models, data, tools, and agents—as controlled technology assets. It also emphasizes testing and monitoring AI workloads under normal and stressed conditions. Those principles apply beyond finance: organizations should know what an agent can access, how it behaves under pressure, and who is accountable for its decisions.
Security guidance from CISA and international partners recommends limiting agent autonomy and avoiding broad access to sensitive data or critical systems. An agent should have only the permissions needed for its assigned task. Credentials should be protected, activity should be logged, and organizations should be able to revoke access quickly if behavior becomes unsafe.
Human approval should match the impact
Not every action needs the same level of supervision. Drafting a private meeting summary may be low risk. Sending a message to a customer, changing a supplier’s payment details, or modifying an access policy can have more serious consequences. Companies can define approval thresholds based on data sensitivity, financial impact, reversibility, and the number of people affected.
Approvals should be meaningful. A person needs enough context to judge the proposed action, including the source data, the agent’s reasoning summary, and any uncertainty. If the interface makes it easy to approve without reading, a human checkpoint may become a formality rather than a control. Teams should review approval patterns and investigate cases where people routinely accept outputs without scrutiny.
Integration and evaluation are the hard work
Connecting an agent to company systems is often harder than building a demonstration. Data may be duplicated across departments, permissions may be inconsistent, and business rules may exist only in employees’ experience. Before deploying an agent, organizations need to map the workflow, define authoritative data sources, and decide how exceptions are handled.
Evaluation should use realistic tasks and measure end-to-end outcomes. Does the agent select the correct record? Does it follow company policy? Does it avoid acting when information conflicts? How often does a person need to correct or redo its work? Teams should test with edge cases and adversarial inputs, then monitor performance after deployment because data, policies, and software integrations change.
Costs also extend beyond model use. Companies need integration engineering, monitoring, data governance, security review, employee training, and ongoing maintenance. A pilot should compare the full operating cost with the current process, including the time people spend supervising the agent. The business case is strongest when an agent improves a measurable workflow without creating a larger burden elsewhere.
Designing a sensible rollout
Organizations can begin with a narrow use case, a small group of users, and permissions that limit possible harm. Run the agent in a read-only or recommendation mode first. Compare its outputs with human decisions, document failure patterns, and fix workflow issues before allowing it to take action. Expand access only after the system meets agreed accuracy and safety criteria.
Employees should be involved in the design because they understand exceptions and downstream effects. Training should explain what the agent can and cannot do, how its work is checked, and how to report a problem. Clear ownership prevents the common failure in which a tool is deployed but no team is responsible for maintaining its data, rules, or integrations.
Enterprise AI is moving from conversation toward delegated action, creating the possibility of digital workers that help complete routine processes. The transition will succeed when organizations define narrow jobs, connect agents to trustworthy data, limit permissions, and measure the results. Autonomy should grow only as reliability and oversight improve. The future of enterprise AI will be shaped not by how many tasks a system can attempt, but by how consistently it can complete useful work within clear boundaries.